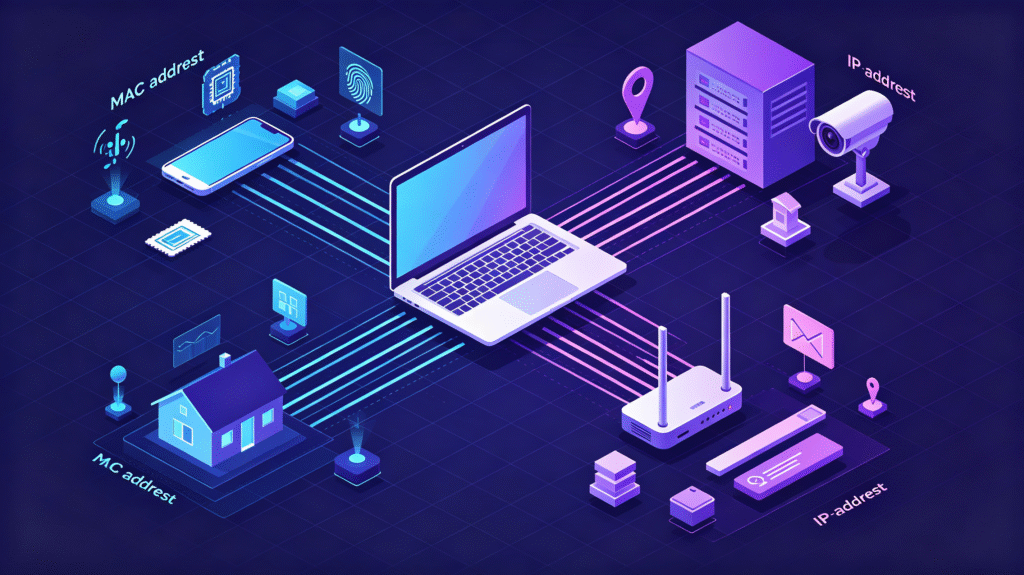
Every device connected to a network carries two distinct identifiers that operate at different layers of the networking stack. The Media Access Control address—commonly known as the MAC address—is a fixed, hardware-embedded identifier assigned by the manufacturer. The Internet Protocol address, or IP address, is a software-defined, routable identifier assigned by a network administrator or Internet Service Provider. These two addresses are not interchangeable alternatives; they are complementary components of a layered addressing architecture that enables data to traverse from a local Ethernet segment to a server on the other side of the world.
For network engineers, infrastructure architects, and professionals managing large-scale web operations, understanding the distinction between MAC and IP addresses is not academic. It determines how traffic is routed, how devices are identified, and how network identity is managed across distributed systems. This article provides a rigorous technical examination of both address types, their roles within the OSI model, the protocols that bind them together, and the practical implications for modern proxy infrastructure. The analysis draws on IPFLY’s comprehensive technical comparison of MAC and IP addresses, which established the foundational framework for this layered addressing model.
What Is a MAC Address?
Definition and Hardware Origins
A MAC address—formally, a Media Access Control address—is a unique identifier permanently assigned to a network interface controller by its manufacturer. Unlike software-configured addresses, the MAC address is burned into the network adapter’s read-only memory during production. This permanence means that if a network interface card is physically moved from one machine to another, the MAC address travels with the hardware. The address remains constant regardless of which network the device joins or which IP address is subsequently assigned.
The term “physical address” is sometimes used interchangeably with MAC address, reflecting its direct association with hardware rather than logical network topology. However, the more precise designation is “data link layer address,” which identifies the layer of the OSI model at which the MAC address operates.
Format and Structure
A MAC address is a 48-bit binary number, conventionally represented as twelve hexadecimal characters grouped into six pairs separated by colons or hyphens. A typical example is 08:00:27:b9:88:74. The structure of this address is not arbitrary. The first three octets—the Organizationally Unique Identifier—identify the manufacturer of the network adapter. The remaining three octets constitute a serial number that the manufacturer assigns to ensure global uniqueness within that organization’s allocated address space.
This hierarchical structure serves a practical purpose. Network management tools and switches can inspect the OUI portion of a MAC address to determine the likely device type without querying higher-layer information. A MAC address beginning with 00:1A:2B, for instance, maps to a specific vendor’s registered prefix, a fact that can be useful for asset inventory and network segmentation.
The Flat Addressing Model
A defining characteristic of MAC addressing is its flat structure. Unlike IP addresses, which encode network topology information, a MAC address carries no hierarchical routing data. It provides no indication of which network the device belongs to, where it is located geographically, or how to reach it from a remote network. The MAC address is purely a local identifier, meaningful only within the broadcast domain of a single Ethernet segment or VLAN.
This flatness is by design. Because MAC addresses are permanent and hardware-based, they cannot be used for routing across internetworks. A router cannot build a global routing table from MAC addresses any more than a postal system could deliver mail using only the recipient’s name without a street address.
Operational Scope: The Local Network
MAC addresses function exclusively within local network boundaries. When a device transmits an Ethernet frame, the destination MAC address in the frame header determines which device on the local segment receives the frame. A switch maintains a MAC address table that maps MAC addresses to physical ports, enabling it to forward frames only to the port where the destination device is connected rather than flooding the entire network.
The broadcast address ff:ff:ff:ff:ff:ff is a special MAC address that every device on a local network accepts. Protocols such as Address Resolution Protocol and Dynamic Host Configuration Protocol use broadcast frames during their initial discovery phases. As IPFLY’s technical comparison notes, MAC addresses operate only within local networks (LAN) and are not visible across the internet, a fundamental limitation that distinguishes them from their IP counterparts.
Permanence and Its Implications
The permanence of MAC addresses has both advantages and limitations. On one hand, it provides a stable identifier for device tracking within a controlled network. On the other hand, it creates a privacy consideration: a device’s MAC address can potentially be used to track its presence across different networks if the address remains unchanged. Modern operating systems address this concern through MAC address randomization, particularly on Wi-Fi interfaces, where the device generates a temporary, randomized MAC address for each network it joins.
For enterprise environments, MAC address filtering is a common access control mechanism, though it is generally considered insufficient as a sole security measure because MAC addresses can be spoofed at the software level on most operating systems. Platform risk systems also record router MAC addresses as part of their account association analysis.
What Is an IP Address?
Definition and Logical Nature
An IP address is a logical, software-assigned identifier that enables devices to communicate across interconnected networks. Unlike the MAC address, which is fixed to hardware, the IP address is assigned through configuration—either manually by an administrator, automatically by a DHCP server, or dynamically by an ISP. The address can change when a device moves to a different network or when the lease period expires and a new address is allocated.
The IP address is the primary mechanism by which packets are routed across the internet. Every packet traveling across a network carries a source IP address and a destination IP address in its header. Routers examine the destination address, consult their routing tables, and forward the packet toward the next hop on the path to its destination.
Format and Versions
The most widely deployed version, IPv4, uses a 32-bit address space, typically displayed in dotted-decimal notation as four octets ranging from 0 to 255—for example, 192.168.1.1. This yields approximately 4.3 billion unique addresses, a pool that was exhausted at the regional internet registry level years ago, though IPv4 remains dominant in practice due to the extensive infrastructure built around it.
IPv6 expands the address space to 128 bits, represented as eight groups of four hexadecimal digits separated by colons. The vastly larger address space of IPv6 eliminates the address exhaustion problem that necessitated techniques such as network address translation in IPv4 networks. IPFLY’s analysis of IPv4 infrastructure explains why the older standard still dominates proxy networks: millions of websites, APIs, and anti-fraud systems are built on an IPv4-first assumption, and an IPv6 address may not be accepted, may not geolocate reliably, or may be treated with suspicion precisely because it is less common .
Hierarchical Addressing and Routing
The IP address incorporates a hierarchical structure that enables efficient routing. Each IPv4 address is divided into a network portion and a host portion, with the boundary determined by the subnet mask. This structure allows routers to aggregate routes: a single routing table entry can represent an entire network of thousands of hosts rather than requiring individual entries for each device.
This hierarchical design is what makes internet-scale routing feasible. Without it, every router on the internet would need to maintain a routing entry for every connected device—an obviously impossible requirement. The IP address’s network-prefix structure allows the routing system to operate on aggregated prefixes, keeping routing tables at a manageable size.
Dynamic Assignment and DHCP
Most devices receive their IP addresses dynamically through the Dynamic Host Configuration Protocol. When a device joins a network, it broadcasts a DHCP Discover message. A DHCP server responds with an offer, and after a brief negotiation, the device receives an IP address along with other configuration parameters such as subnet mask, default gateway, and DNS server addresses. The lease is time-limited; when it expires, the device must renew it or obtain a new address.
DHCP introduces a layer of abstraction between the device’s permanent MAC address and its current IP address. The DHCP server may maintain a mapping of MAC addresses to previously assigned IP addresses, allowing a device to receive the same IP address each time it joins the network, but this is a server-side convenience rather than a requirement of the protocol.
IPv4 and IPv6 Coexistence
Despite the technical superiority of IPv6 in terms of address space, IPv4 remains the dominant protocol for proxy infrastructure and web operations. The reason is compatibility: millions of websites, APIs, and anti-fraud systems are built on IPv4-first assumptions. An IPv6 address may not be accepted by a target server, may not geolocate reliably, or may be treated with heightened suspicion precisely because it is less common in certain contexts. IPFLY’s infrastructure reflects this reality, with a residential IPv4 pool exceeding 90 million addresses spanning more than 190 countries and regions.
MAC Address and IP Address: A Structured Comparison
| Characteristic | MAC Address | IP Address |
| OSI Layer | Data Link Layer (Layer 2) | Network Layer (Layer 3) |
| Address Length | 48 bits (6 bytes) | 32 bits (IPv4) / 128 bits (IPv6) |
| Assignment | Manufacturer, at production | Network administrator or ISP |
| Permanence | Fixed to hardware | Dynamic; changes with network |
| Scope | Local network (LAN) only | Global (routable across internetworks) |
| Routing Capability | None; flat addressing | Hierarchical; enables routing |
| Visibility | Not visible beyond local segment | Visible to every server that receives a packet |
| Format Example | 08:00:27:b9:88:74 |
203.0.113.45 |
The table above summarizes the essential distinctions. The most consequential difference for network operations is the visibility gap: MAC addresses remain confined to the local network, while IP addresses are exposed to every destination server on the public internet. This asymmetry is the foundation of IP-based reputation systems, geolocation services, and anti-fraud mechanisms that govern access to web resources.
How MAC and IP Addresses Work Together
ARP: The Bridge Between Layers
The Address Resolution Protocol is the mechanism that connects the logical IP address space to the physical MAC address space. When a device needs to send an IP packet to another device on the same local network, it knows the destination IP address but not the corresponding MAC address. ARP resolves this gap through a broadcast query: the sending device broadcasts an ARP request asking, in essence, “Which device owns this IP address?” The device with the matching IP address responds with its MAC address, and the sender caches this mapping for future use.
The ARP cache maintains a table of recently resolved IP-to-MAC mappings. Entries in this table have a limited lifetime—typically around four hours—after which they are discarded and must be re-resolved if needed. This timeout exists because IP addresses can change: a device may leave the network, another may take its IP address, and the MAC address associated with that IP address may consequently change.
The Journey of a Packet
Consider a request from a workstation to a web server on the internet. The application layer generates an HTTP request. The transport layer encapsulates it in a TCP segment. The network layer adds an IP header containing the source and destination IP addresses. The data link layer adds an Ethernet header containing the source and destination MAC addresses. At this point, the destination MAC address is not the web server’s MAC address—it is the MAC address of the default gateway or the next-hop router.
The frame travels across the local network to the router. The router strips the Ethernet header, examines the destination IP address, and consults its routing table to determine the next hop. It then constructs a new Ethernet frame with a new destination MAC address—the MAC address of the next router—while the IP addresses in the packet header remain unchanged end to end. This process repeats at each hop until the packet reaches the network where the destination server resides. Finally, the last router uses ARP to resolve the server’s MAC address and delivers the frame to the correct physical interface.
Complete Proxy IP Fundamentals
Build a full proxy knowledge framework — from core principles to protocol selection
Why Both Addresses Exist
The dual addressing scheme is not redundant; each address serves a purpose that the other cannot fulfill. The IP address provides the globally routable, hierarchically structured identifier necessary for internetwork communication. The MAC address provides the locally significant, hardware-stable identifier necessary for delivery within a single network segment. Attempting to route internet traffic using MAC addresses alone would be impossible because MAC addresses contain no network topology information. Conversely, using IP addresses alone would require the network layer to manage hardware-level delivery, which is the proper domain of the data link layer.
IP Address Reputation: Why It Matters Beyond Routing
The Reputation Layer
An IP address is more than a routing label. Every IP address carries a reputation that destination servers evaluate before granting access. This reputation is derived from multiple signals: the autonomous system number that announces the address range, the geographic location associated with the address, historical behavior patterns observed from that address, and the type of network from which the address originates—residential, mobile, or datacenter.
Anti-fraud systems analyze these signals to distinguish legitimate users from automated traffic. A residential IP address assigned to a consumer broadband connection carries a fundamentally different risk profile than an IP address originating from a cloud hosting provider. The former blends into the ordinary background of internet traffic; the latter may trigger additional verification challenges because datacenter IP ranges are disproportionately associated with automated activity.
The Four Dimensions of IP Risk
Sophisticated fraud detection systems evaluate IP addresses across multiple dimensions rather than relying on static blacklists. Activity measures how many devices connect through a single IP address: a residential IP address associated with one or two devices appears normal, while an address serving hundreds of devices within a short period likely indicates shared or abusive usage. Geolocation examines the number of distinct locations associated with an address; an IP address that appears in multiple cities or countries over a brief period suggests manipulation. Range assesses the distance between observed locations, where rapid, large-distance movements almost certainly indicate masking. Location persistence measures how long an address remains associated with a given location, with low persistence potentially signaling rotating infrastructure.
These dimensions create a layered risk profile that helps systems distinguish genuine users from suspicious actors. For businesses that depend on reliable access to web data—whether for price monitoring, ad verification, or market research—managing these reputation signals is as important as managing the technical connectivity itself.
Proxy Infrastructure and IP Identity Management
The Role of Proxy Networks
When an organization needs to make requests to external servers while presenting a consistent, trustworthy network identity, proxy infrastructure becomes essential. A proxy network substitutes the source IP address that the destination server observes. Instead of seeing the originating organization’s address—which may be associated with a datacenter or a geographic region that triggers restrictions—the server sees the proxy’s address, which can be selected to align with the expected profile of a legitimate user.
Residential proxies are particularly valuable in this context because their IP addresses are assigned by consumer ISPs and associated with real physical locations. these proxies use real IP addresses from everyday internet users, making online actions appear as normal, human traffic rather than automated access . Requests originating from residential IP addresses are evaluated by target platforms as legitimate user traffic rather than as automated access, which reduces the likelihood of encountering blocks or silent denials.
IPFLY’s Approach to IP Resource Management
IPFLY operates a distributed proxy network built on a pool of over 90 million residential IPv4 addresses spanning more than 190 countries and regions. IPFLY’s infrastructure documentation details how the platform transforms a pool of raw numeric addresses into a trusted, scalable access layer through city-level targeting, sticky sessions, and SOCKS5 encapsulation . The infrastructure is designed to support both dynamic and static use cases through a unified platform. For operations requiring high-frequency rotation, Dynamic Residential Proxies provide per-request or session-based IP assignment, with rotation triggers that adapt to request patterns and failure signals. For operations requiring a consistent identity over time, Static Residential Proxies provide dedicated ISP-registered addresses that remain fixed for the duration of the engagement.
The platform’s routing engine assigns IP addresses based on task type: single requests receive fresh addresses, session-based workflows maintain sticky IP binding for a defined duration, and parallel tasks receive distributed allocations to balance load across the pool. This task-aware allocation ensures that the IP behavior observed by destination servers aligns with expected patterns of legitimate user activity.
For businesses requiring large-scale data acquisition or high-concurrency operations, Datacenter Proxies offer low-latency, high-throughput connectivity with response times averaging 0.2 seconds and success rates maintained at 99.9%. These dedicated IPs are suitable for scenarios where speed and consistency are prioritized over the residential reputation profile.
Sticky Sessions and Session Consistency
Many web workflows—account logins, multi-step checkout processes, and sequential browsing sessions—require the same IP address to be maintained across multiple requests. IPFLY’s sticky session capability assigns a session identifier to an IP address and maintains that mapping for a user-defined duration, ranging from minutes to an entire work shift. When the session expires, the IP address is released back into the pool and rotated, preserving the benefits of dynamic allocation while supporting workflows that demand continuity.
This session-based binding is particularly relevant for e-commerce operations, where maintaining a consistent IP address throughout a purchase flow is often necessary to avoid triggering fraud detection systems that flag sudden IP changes during transactional sequences.
Practical Applications and Use Cases
E-Commerce Price Monitoring
Retailers and market research firms monitor competitor pricing across multiple regions. A request originating from a datacenter IP address may be blocked or served different content than a request from a residential IP address in the target market. IPFLY’s residential proxies enable geographic targeting at the city level, allowing operations to observe pricing as a local user would see it. The sticky session feature maintains consistent identity across a browsing session, enabling the collection of complete product catalog data without mid-session interruptions.
Ad Verification
Digital advertising verification requires confirming that ads are displayed correctly across different geographic markets and device profiles. Ad networks often serve different creatives based on the viewer’s IP address. A verification system that appears to originate from a datacenter may receive placeholder content or no ad at all. Residential IP addresses from the target market ensure that the verification request is treated as a genuine user impression.
Multi-Account Management for Social Platforms
Platforms such as Instagram evaluate a combination of signals when assessing account legitimacy, with IP address carrying significant weight. An IP address that changes location abruptly, that is shared across dozens of accounts, or that is associated with a datacenter range will raise the platform’s risk score for every account using it. Static residential proxies provide dedicated, ISP-registered IP addresses that remain consistent for each account, allowing the platform to build a stable trust profile over time.
Data Acquisition at Scale
Organizations that collect public web data—for competitive intelligence, academic research, or AI model training—face the challenge of maintaining access while respecting the technical boundaries that target servers enforce. Dynamic residential proxies with per-request rotation distribute requests across a large pool of IP addresses, preventing any single address from accumulating suspicious activity patterns. IPFLY’s load balancing mechanism continuously evaluates node performance and adjusts routing to avoid overused addresses and regional bottlenecks.
Compliance and Responsible Network Operations
The technical capabilities of proxy infrastructure must be exercised within appropriate legal and ethical boundaries. Proxy networks are designed to support legitimate business operations: market research, ad verification, brand protection, and data collection from publicly accessible sources. They are not tools for circumventing legal restrictions, engaging in fraudulent activity, or violating the terms of service of platforms in ways that cause harm.
Organizations deploying proxy infrastructure should maintain clear internal policies regarding acceptable use, ensure that data collection activities comply with applicable regulations including data protection laws, and respect the technical measures that websites implement to manage access. The goal of responsible proxy usage is not to evade detection but to present an accurate, legitimate network identity that reflects the genuine nature of the requesting entity’s operations.
IPFLY’s platform is designed for enterprise-grade business applications, with support for HTTP, HTTPS, and SOCKS5 protocols, unlimited concurrency for large-scale operations, and API-based access for integration with existing data pipelines. The service supports city-level geo-targeting and ISP-level selection, enabling precise control over the network identity presented to destination servers.
Summary: The Foundational Role of Addressing in Network Operations
The MAC address and IP address represent two distinct layers of the networking stack, each solving a problem the other cannot address. The MAC address provides a permanent, hardware-anchored identifier for local network communication, ensuring that Ethernet frames reach the correct physical interface within a broadcast domain. The IP address provides a dynamic, hierarchically structured identifier for internetwork routing, enabling packets to traverse the global internet from source to destination.
The relationship between these addresses is mediated by protocols such as ARP, which dynamically resolves the mapping between logical and physical addresses as needed. This layered addressing architecture is what makes internet-scale communication possible: routing operates on aggregated IP prefixes rather than individual device identifiers, while local delivery operates on hardware-stable MAC addresses that remain consistent regardless of network configuration changes.
For organizations that depend on reliable access to external web resources, the IP address is not merely a routing mechanism—it is an identity that destination servers evaluate, classify, and judge. Managing that identity through residential proxy infrastructure ensures that requests are attributed to network locations that align with legitimate user profiles. IPFLY’s residential, static residential, and datacenter proxy offerings provide distinct tools for different operational requirements, all built on a shared infrastructure of over 90 million IP addresses across more than 190 countries and regions.
Take Control of Your Network Identity
Whether your operations require the geographic precision of city-level residential targeting, the session stability of sticky IP binding, or the raw throughput of dedicated datacenter connectivity, IPFLY’s platform provides the infrastructure to manage IP identity at scale. The network layer is where access is granted or denied—and the address you present there determines the outcome.
Explore IPFLY’s Residential Proxies → for dynamic, rotation-ready IP pools. For workflows that demand a consistent, ISP-registered address.
Static Residential Proxies → deliver dedicated IPs with unlimited traffic. When speed and concurrency are the priority.
Datacenter Proxies → provide low-latency performance at scale.
Create your IPFLY account → to begin configuring your proxy infrastructure.